The AppSec bottleneck isn’t detection. It’s remediation
Why triage and remediation now set the pace
Effective March 27, 2026, HackerOne paused accepting new submissions to its Internet Bug Bounty program. Its explanation pointed to a growing imbalance: AI-assisted research is increasing the speed and coverage of vulnerability discovery, while open-source maintainers haven’t gained matching capacity to assess and remediate those findings.
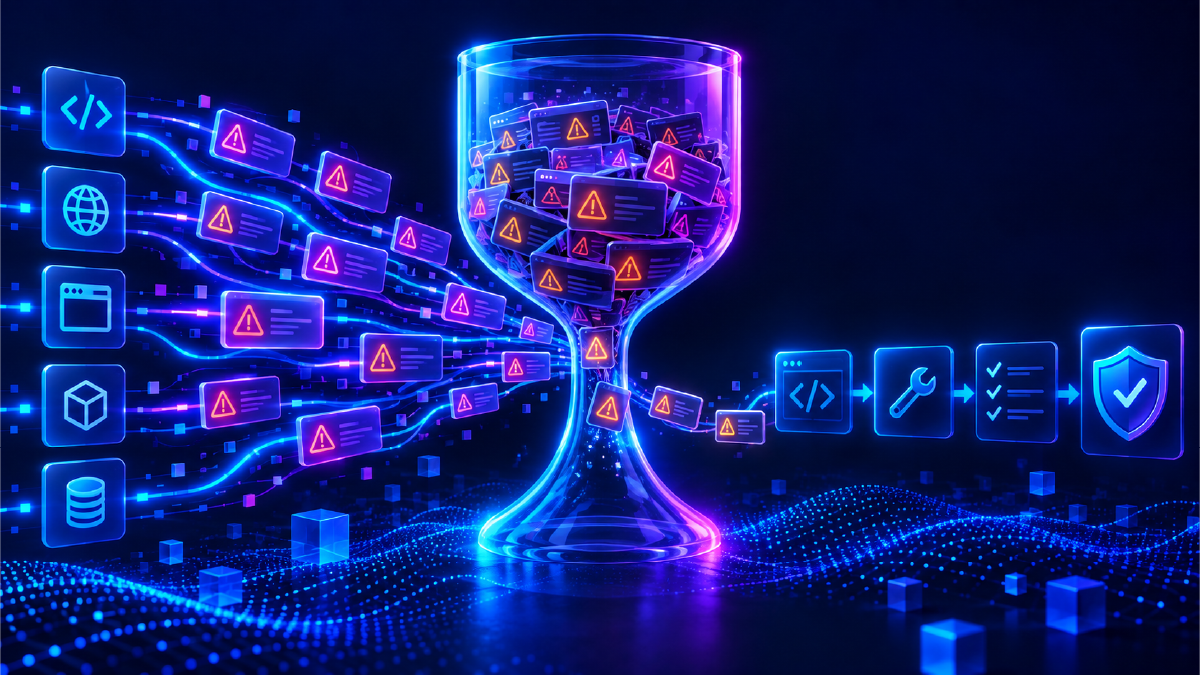
The same imbalance shows up in enterprise AppSec. Teams already generate findings from source code, running applications, APIs, and open-source components. Adding more discovery without improving triage and AppSec remediation can produce a larger backlog rather than reduce risk.
More findings don’t automatically mean better security
Security improves when teams can determine which findings matter, route them to the right owners, and resolve them before they create risk in production. That’s why the operational question is shifting from “Can we find more?” to “Can we act on what we already know?”
Frontier AI models are accelerating this shift. Anthropic’s Project Glasswing gives selected organizations access to a frontier model for defensive security work, including finding vulnerabilities in critical and widely used software. For enterprise AppSec programs, the harder problem is applying new techniques while maintaining the coverage, repeatability, policy enforcement, and evidence a large application portfolio requires. As detection capabilities expand, the systems around them matter more.
A layered AppSec architecture starts with repeatable testing
Established testing methods remain the foundation because each addresses a different part of application risk. OpenText™ Fortify™ SAST analyzes source code to find vulnerabilities early in the software development lifecycle, OpenText™ Fortify™ DAST tests running applications, APIs, and services in deployed environments, and OpenText™ Fortify™ Software Composition Analysis identifies open-source vulnerabilities, license obligations, and component health risks.
Together, they provide repeatable coverage across proprietary code, deployed applications, APIs, and open-source dependencies, and they generate the findings and evidence that prioritization, remediation, and governance depend on. For more on pairing static and dynamic testing, read 5 Reasons Why SAST + DAST with Fortify Makes Sense.
Where AI helps AppSec remediation
OpenText™ Fortify™ Remediation Aviator™ applies AI to the auditing and remediation work that follows SAST. It reviews findings, helps distinguish true positives from false positives, explains results in context, and provides remediation guidance. For eligible findings, it can also generate fixes and apply them automatically where it’s safe to do so. It can also correlate related SAST and DAST findings, giving teams more context when a weakness found in source code also appears in a running application.
OpenText first deployed this approach across its own enterprise application environment. In the first eight weeks, OpenText onboarded 1,500 applications, audited more than 300,000 findings, and reduced mean time to triage by 70%, saving an estimated 3 million minutes of manual review time. These results are specific to OpenText’s internal deployment and don’t guarantee identical outcomes for every organization. They do show the kind of operational evidence AppSec leaders should expect: a defined workflow, measurable improvements, and results that extend beyond a limited demonstration. See the full deployment results in AI AppSec, Proven at Scale.
Build the program around action
A more complete AppSec operating model combines three layers. Repeatable testing provides coverage across code, applications, APIs, and open-source components. AI assistance reduces manual analysis and remediation effort. Governance connects findings with policy, prioritization, evidence, and reporting. The goal is to help development and security teams decide what needs action and resolve it before the backlog outpaces their capacity. Organizations that strengthen triage and remediation can turn broader testing into better security outcomes rather than more noise.