The AppSec ROI reckoning: Moving from AI hype to measurable value
As AI spending faces greater scrutiny, AppSec leaders must prove measurable results and governance.
AppSec ROI is coming under sharper scrutiny as AI budgets move beyond experimentation. KPMG’s Global AI Pulse for the third quarter of 2026, a survey of more than 2,100 senior leaders across 20 countries, territories, and jurisdictions, finds that competitive advantage is shifting from adopting AI to running it effectively. The data shows a clear pattern. Among organizations reporting established AI ROI, 86% operate a formal cross-functional or enterprise-wide AI management layer. That compares with 31% of organizations still experimenting with AI.
The research covers enterprise AI broadly, but the lesson applies directly to application security. Adoption alone is not the measure. The questions that matter are what improved, how much effort was saved, and whether the organization can verify the result.
A new AI feature is not automatically a durable investment
AI can help address real AppSec challenges. Security teams often face more findings than they can manually review, while developers need clearer guidance on which issues matter and how to fix them.
The value of an AI capability, however, should not be judged by the quality of a demonstration or the number of features announced. Buyers should ask how the capability fits into the broader application security program and whether teams can operate and govern it at scale, rather than simply switch it on.
Does it work with established static application security testing (SAST), dynamic application security testing (DAST), and software composition analysis (SCA) processes? Does it help teams prioritize or remediate findings? Can its use be controlled, measured, and audited? Most importantly, can the organization show that it improved an outcome?
Those questions separate a capability an organization can manage from a short-term reaction to market hype.
What sustained investment looks like
OpenText began adding generative AI capabilities to the OpenText™ Fortify™ portfolio in 2023. Since then, OpenText has introduced AI capabilities across the portfolio to support vulnerability analysis, triage, remediation, and emerging risks in AI applications.
That sustained approach matters because models, providers, and development practices continue to change. KPMG’s latest research examines how organizations are linking cybersecurity, model sovereignty, and provider dependency as related risks to resilience. For AppSec leaders, that means building on a foundation that combines established testing with AI where it delivers a clear advantage, without abandoning the workflows and controls the organization already relies on.
OpenText has also tested these capabilities in its own software environment. During the first eight weeks of an internal deployment, Fortify™Remediation Aviator™ audited more than 300,000 findings across 1,500 applications, reduced mean time to triage by 70%, and saved an estimated three million minutes of manual review time.
These results do not guarantee the same outcome for every organization. They do demonstrate the kind of evidence buyers should request when evaluating an AI investment: defined scope, measurable results, and a clear explanation of how those results were calculated.
Governance turns AI capability into AppSec value
The KPMG findings point to where durable value is made. Organizations that report established ROI are far more likely to have formalized how AI is managed across the business. KPMG frames AI at scale as a management challenge: Organizations need to control model provenance and access, coordinate usage, and track costs.
AppSec needs the same discipline. Organizations must decide which actions can be automated, which require human review, how exceptions are handled, and what evidence is retained for security and compliance teams.
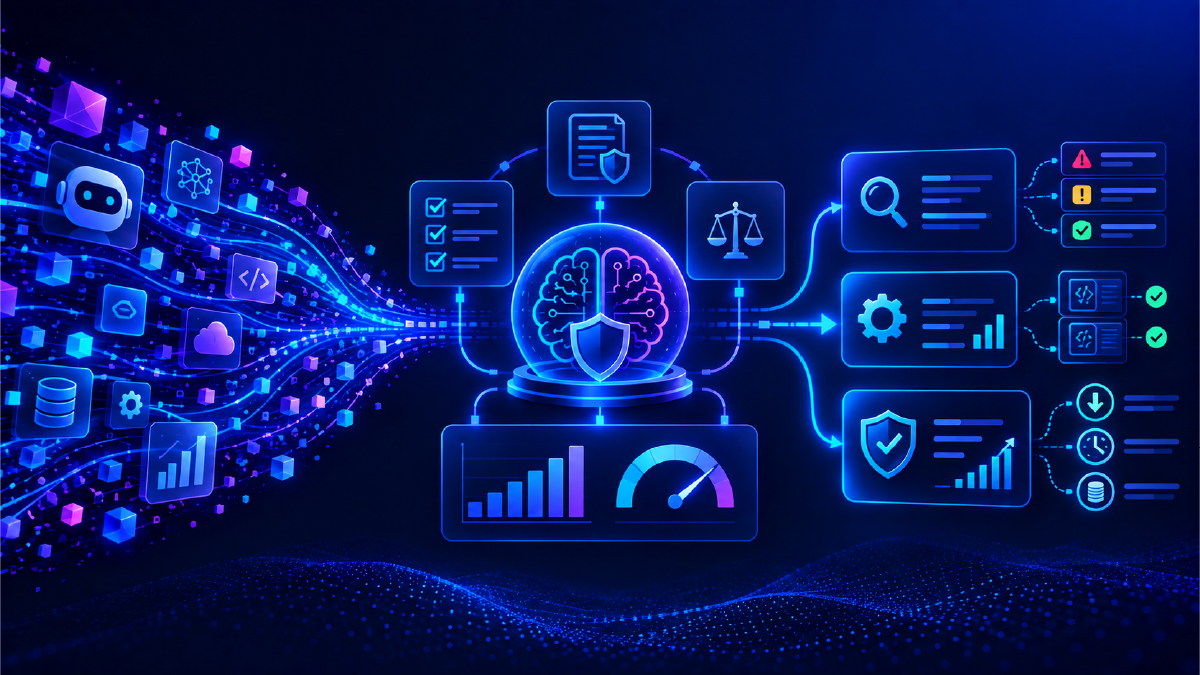
Those decisions should be part of the architecture, not an afterthought. Fortify supports this approach by combining application security testing with centralized management, risk prioritization, policy, reporting, and deployment options that allow organizations to adopt AI at a level appropriate for their environment.
The goal is not to add the most AI features. It is to improve security outcomes without losing control of the process.
How to assess AppSec ROI
Before expanding an AI investment, AppSec leaders should be able to document five things. The first is scope: which applications, findings, and workflows were included. The second is outcome: whether the capability improved triage time, remediation time, developer productivity, or risk reduction. The third is method: how the baseline and the resulting improvement were calculated.
The fourth is governance: which actions require human review, and what evidence is retained. The fifth is scale: whether the organization can reproduce the result across teams and environments. A capability that cannot be documented across all five is still an experiment, not an investment.
As AI spending receives greater scrutiny, the strongest AppSec investments will be the ones organizations can explain clearly. What improved? How was it measured? What controls remain in place?
Teams that can answer those questions with evidence have moved beyond AI hype and toward durable AppSec value.