Agentic AppSec: Securing code that agents help write
As agents take action, AppSec controls must follow.
Software development is shifting from AI-assisted suggestions to agent-driven actions. Coding agents can work across repositories, call development tools, and complete multi-step tasks under human oversight. These workflows can accelerate development, but they also change where and how security controls must operate. Agentic AppSec brings established security testing and governance into these workflows.
The aim is consistent security testing, review, and governance for code, dependencies, and application changes, whether a person or an agent helped create them. That shouldn’t require slowing agents down or moving every team onto the same assistant.
Software accountability doesn’t change with the author
The reporting obligations in the European Union Cyber Resilience Act (CRA) took effect on September 11, 2026. Manufacturers must submit an early warning within 24 hours of becoming aware of an actively exploited vulnerability or a severe incident affecting the security of their product, followed by a full notification within 72 hours. Broader CRA obligations apply from December 11, 2027.
The regulation doesn’t prescribe a particular AppSec tool or development model. It does reinforce the need to understand the security of products with digital elements, respond to exploited vulnerabilities, and maintain processes that support timely reporting. Those responsibilities apply whether a developer writes the code, an assistant suggests it, or an agent helps change it.
Bring approved AppSec workflows to coding agents
OpenText Fortify Agent Skills are open-source skills that teach supported coding agents how to work with Fortify. The repository provides skills for scanning with static application security testing (SAST), dynamic application security testing (DAST), and software composition analysis (SCA), along with vulnerability triage, remediation, dependency upgrades, continuous integration and continuous delivery (CI/CD) integration, and Fortify command-line interface (CLI) tasks. It identifies support for Claude Code, OpenAI Codex, Gemini CLI, GitHub Copilot, and other compatible agents.
This gives the coding agent access to approved Fortify context without making it the system of record. Depending on the selected skill and configured Fortify environment, the agent can retrieve findings, follow defined analysis steps, prepare remediation changes, and return the proposed work for developer review.
The advantage is context. An agent working from source code alone has to infer security risk. With Agent Skills, teams can give it Fortify findings and a defined workflow. Building AI-Powered AppSec Momentum for Defenders describes how these skills can support exploitability analysis, application onboarding, and more efficient use of coding agents.
How agentic AppSec works in practice
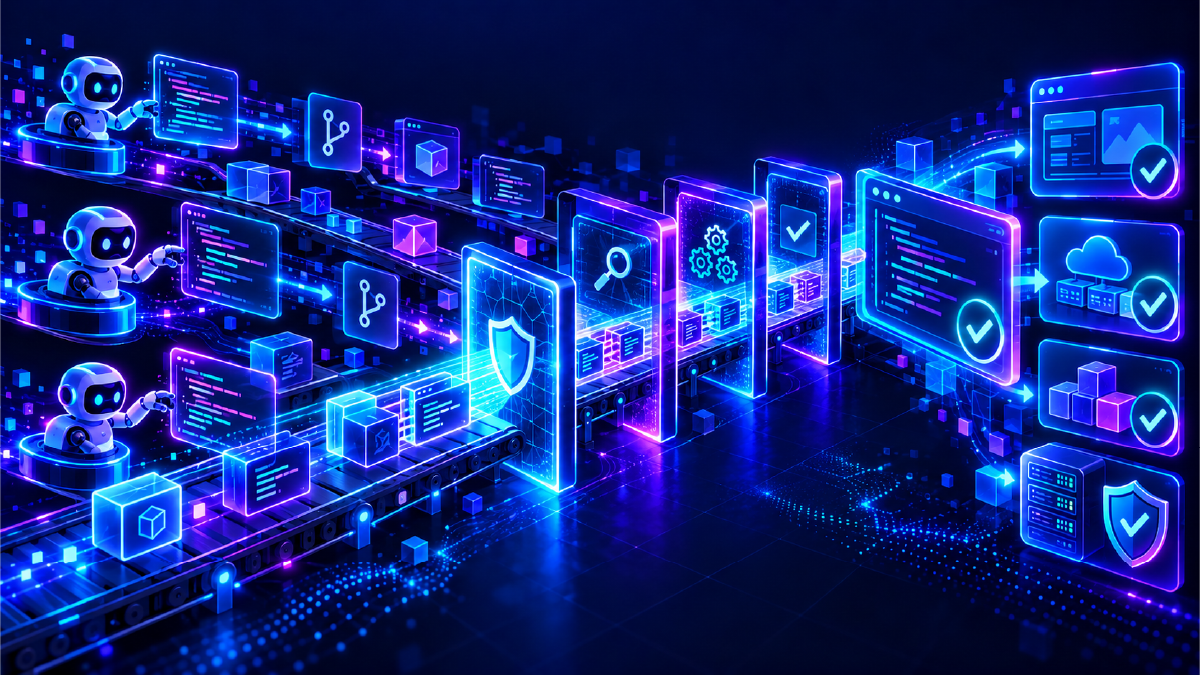
A coding agent can receive a development task, interact with repositories and tools, and prepare code changes. The security workflow around that agent should stay independent of its judgment, and each part of the workflow plays a distinct role.
OpenText™ Fortify™ SAST analyzes source code across 45+ languages and integrates with development and CI/CD workflows. OpenText™ Fortify™ DAST tests running applications, APIs, and services by simulating real-world attacks. OpenText Fortify Software Composition Analysis identifies open-source vulnerabilities, license obligations, and component health risks. Together, they produce repeatable findings across code, running applications, APIs, and open-source components.
OpenText™ Fortify™ Remediation Aviator™ adds AI-assisted auditing and remediation for SAST findings. It helps separate true positives from false positives, explains findings in context, provides code-level remediation guidance, and can generate fixes and apply them automatically to eligible findings where it’s safe to do so.
Agent Skills bring that Fortify context into the coding agent’s workflow, so the agent can understand findings and prepare changes for human review. Policy decisions, exceptions, evidence, and reporting stay within the broader AppSec program instead of being delegated to the agent.
A practical operating model for coding agents
Agent-driven development increases the value of security controls that operate consistently across developers, repositories, pipelines, and AI-assisted workflows. Teams can apply a practical four-part model. First, use proven testing to find risk across the software lifecycle. Second, give coding agents approved AppSec context and workflows. Third, keep human review, policy, evidence, and reporting around consequential actions. Finally, use AI-assisted auditing and remediation where it reduces manual effort without giving up control.
Coding agents can help teams move faster. OpenText Fortify helps organizations find and fix risk in what those workflows produce and apply consistent security controls across modern development environments. For a closer look at where agentic analysis fits, Applying Agentic Analysis to Real AppSec Problems shows how it can complement established scanning for complex logic and design flaws.